Sfoglia categorie
Esplora
Fiverr Pro
Italiano
$
USD
Web Application Penetration Tester API Security Bug Bounty Hunter
Why should we work together?
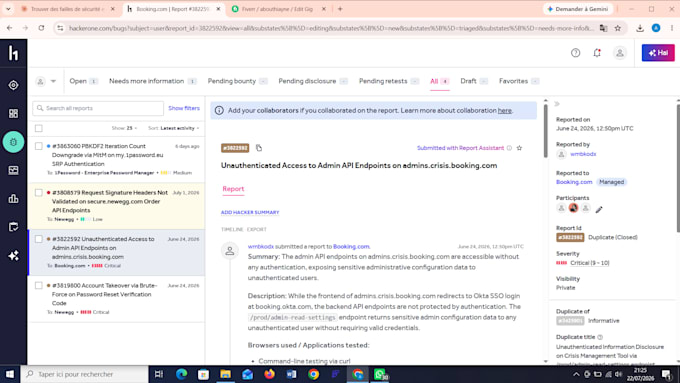
1. I am a security researcher with verified reports on HackerOne for Booking.com, Newegg and 1Password.
2. I test your application manually like a real attacker, not just automated scanners.
Send me your website URL and authorization to test.
I will provide you with the following:
- Full security assessment of your web application
- API endpoint testing for authentication and access control flaws
- Business logic vulnerability testing
- Professional PDF report with severity ratings
- Step-by-step remediation recommendations
Tools: Burp Suite, Kali Linux, manual testing.
If you have any questions, I invite you to contact me before ordering.

What do you need from me to start testing?
I need the URL of your application, test account credentials if applicable, and written authorization to perform the security test.
Will your testing damage my website or data?
No. I use non-destructive testing methods. I identify vulnerabilities and document them without causing any damage to your application or data.
What will I receive at the end?
A professional PDF report with all vulnerabilities found, severity ratings, screenshots as proof, and step-by-step instructions to fix each issue.
How long does the security test take?
Basic scan takes 3 days, full audit takes 7 days, and deep penetration test takes 14 days depending on the size of your application.