Sfoglia categorie
Italiano
$
USD
Connettiti alla tua IA


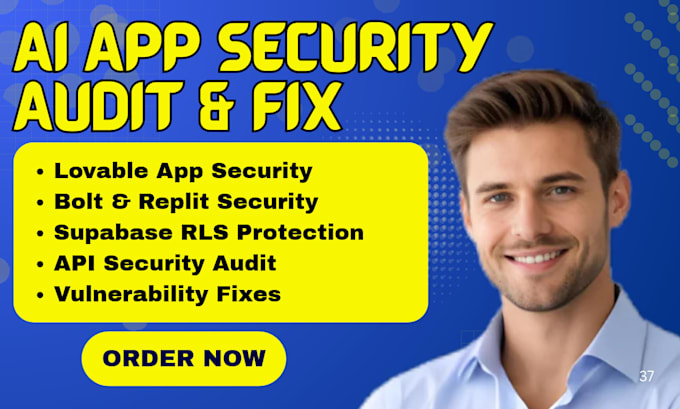
Is your AI-generated app secure enough for launch?
I will audit and fix security vulnerabilities in your Lovable, Bolt, Replit and Supabase applications.
AI-built apps can contain security gaps that expose sensitive data, user accounts, APIs and databases. I help identify and fix these issues so your application is safer, more reliable and better prepared for production.
WHAT I OFFER
WHY WORK WITH ME?
I focus on practical security improvements, clear communication and carefully tested fixes. Whether you built your app with Lovable, Bolt, Replit or Supabase, I can help review its security and address agreed vulnerabilities.
LET'S SECURE YOUR APP!
Contact me before ordering so we can discuss your platform, security concerns and project requirements.
AI APP DEVELOPER, LOVABLE, BASE44 AND WEB SOLUTIONS
Lingue
Can you audit apps built with Lovable, Bolt, Replit, and Supabase?
Yes! I can review applications built with Lovable, Bolt, Replit, and Supabase, identify security weaknesses, and recommend or implement suitable fixes.
What security issues can you identify and fix?
I can help with exposed API keys, weak authentication, authorization issues, insecure database permissions, Supabase RLS policies, API vulnerabilities, and other common application security risks.
Do you provide Supabase Row Level Security (RLS) fixes?
Yes. I can review Supabase Row Level Security policies, database access permissions, and user access controls to help prevent unauthorized access to sensitive data.
Can you secure my AI-generated app before launch?
Absolutely! I can review your application's authentication, APIs, database permissions, environment variables, and other important security areas to help prepare it for production.
Will you fix the vulnerabilities you discover during the audit?
Yes. Depending on your selected package, I can fix agreed security issues, review the changes, and provide documentation of the work completed.
What do you need to start the security audit?
I need your app URL, the platform used, a description of your security concerns, and relevant code or repository access. Never send passwords or private API keys through Fiverr messages.
Can you audit a large or complex AI-powered application?
Yes. Please contact me before ordering with details about your application, technology stack, database, and security requirements so I can assess the scope and recommend the right package.