Sfoglia categorie
Esplora
Fiverr Pro
Italiano
$
USD


Apps built with Lovable, Bolt, Cursor and similar tools often go live with database rules that are missing or too loose. In practice that can mean anyone who opens your site can read other users' rows, or a logged-in user can change data that isn't theirs.
I test your app the way an attacker would, with your permission. First as a visitor using only the public key that's already in your site's code, then as two different logged-in users. For each table I check who can read, create, change and delete. I also go through your Row Level Security policies and storage buckets.
What you get:
- A short report: each table, who can do what today, and what should change
- SQL migrations that fix the problems, sent as a file or a pull request
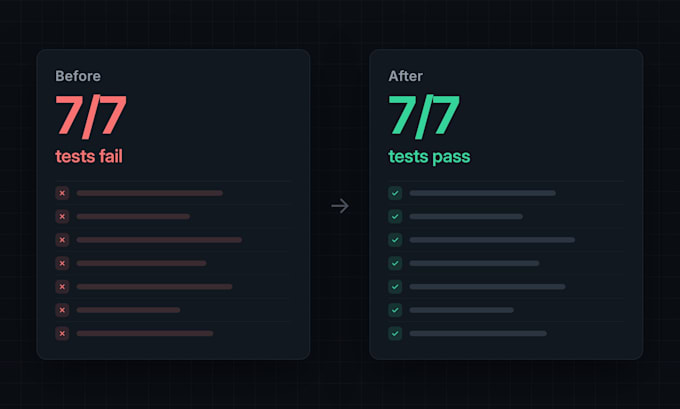
- A test for each fix that fails before the change and passes after it
I don't need your service role key. For the audit I need your app URL, two test accounts, and access to your code or Supabase project.
A full worked example, with the report and the tests, is in my portfolio.
If the problem turns out to be bigger than the package, I'll tell you before doing anything extra.
Nextjs, Supabase Developer, Fixing AI Built Apps for Production
Lingue
Do you need my service role key?
No. I test with the public key your site already sends to every visitor and two test accounts you create, and read your setup through your GitHub repo or a Developer invite to your Supabase project. Fixes come as SQL you apply, or as a pull request.
Will this touch my real data?
Read checks run against your live app, but I only create, change or delete rows that the test accounts make, and I remove them at the end.
What if my app has more than 10 tables?
Message me before ordering with the number of tables, and for Advanced, the number of API routes. Each package covers up to 10 tables, and Advanced covers up to 10 API routes. For bigger apps I'll send a custom offer.
Can you fix things outside the database?
The Advanced package covers login, API routes and deployment. For anything else, ask first.
My app wasn't built with Lovable. Does this still apply?
Yes. What I check is the Supabase side: tables, policies, storage and functions. It doesn't matter which tool or framework built the frontend.