Sfoglia categorie
Italiano
$
USD
Connettiti alla tua IA
Penetration Tester, Cybersecurity Engineer
Is your web application secure against real-world attacks?
I will perform web application penetration testing to identify and validate security vulnerabilities, assess their potential impact, and provide actionable remediation recommendations.
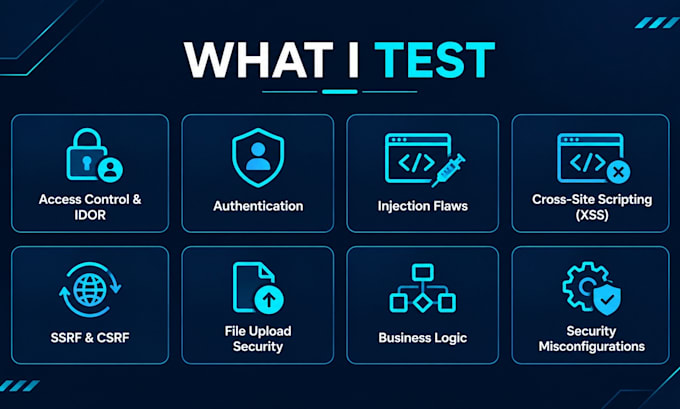
What I test:
Broken access control and IDOR
Authentication and session management
SQL Injection and other injection flaws
Cross-Site Scripting (XSS)
Cross-Site Request Forgery (CSRF)
Server-Side Request Forgery (SSRF)
File upload vulnerabilities
Security misconfigurations
Business logic flaws
OWASP Top 10 risks
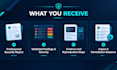
What you will receive:
A professional security report
Vulnerability descriptions and severity ratings
Evidence and reproduction steps
Potential impact assessment
Practical remediation recommendations
I combine automated tools with manual testing to validate findings and reduce false positives.
Please contact me before ordering so we can agree on the application's scope, testing requirements, and delivery timeline.
Security testing is performed only on applications for which you have proper authorization.
Applicazione di testing:
Applicazione web
Tecnologia di sviluppo:
.NET
•
Java
•
JavaScript
•
PHP
•
Python
Dispositivo:
PC
•
Linux
What does your penetration testing service include?
I combine automated scanning with manual security testing to identify and validate vulnerabilities in web applications. Testing may cover access control, IDOR, authentication, injection flaws, XSS, SSRF, security misconfigurations, and business logic issues, depending on the agreed scope.
Will I receive a security report?
Yes. You will receive a security report documenting validated findings, severity, technical evidence, reproduction steps, potential impact, and remediation recommendations, according to your selected package.
Do you test authenticated web applications?
Yes. Authenticated testing is available when required test accounts and access are provided. Please contact me before ordering to confirm authentication requirements and the testing scope.
What does one revision include?
One revision covers reasonable corrections to the report or clarification of existing findings and recommendations. It does not include a new penetration test, additional targets, expanded scope, or retesting after remediation. Retesting can be arranged separately.
Do you offer retesting after vulnerabilities are fixed?
Retesting can be arranged as a separate service to verify whether reported vulnerabilities have been properly addressed. Please contact me to discuss the scope and pricing.
What do you need before starting the assessment?
Please provide the target URL, agreed testing scope, relevant technical details, authentication requirements, and any testing restrictions. You must own the application or have explicit authorization to have it tested. Please contact me before ordering to confirm the scope.