I will perform a professional penetration test on your web app or network

D
danibs
D
danibs
Daniele T
Alcune informazioni sono riportate in lingua inglese.

Informazioni su questo servizio

Is your website or web application secure? Do you know what an attacker could actually do with it?


I am a certified offensive security professional with 5 industry certifications (eCPPT, eWPT, eJPT, CRTA, ICCA) currently working as a SOC Analyst. I perform manual penetration testing to find real, exploitable vulnerabilities in your systems before real attackers do.


What I test:

  • OWASP Top 10 (injection, XSS, broken auth, IDOR, SSRF, misconfiguration)
  • - Authentication and session management
  • - Access control and business logic flaws
  • - API endpoints
  • - Network services and open ports
  • - Active Directory (on request)

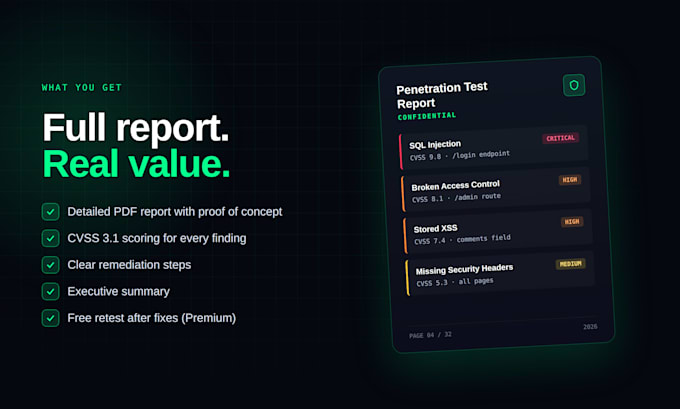
What you get:

  • Detailed PDF report with findings, severity (CVSS 3.1) and proof of concept
  • - Clear remediation steps for each finding
  • - Executive summary for non-technical stakeholders (Standard and Premium)
  • - Free retest after your team applies the fixes (Premium only)

Before we start you must provide written authorization to test the target scope. I only test systems you own or have explicit permission to test.


Message me before ordering with your target URL or IP range and I will confirm the scope and pricing fit your needs.

Rispettare i diritti di terzi

Ricorda che è contrario alle politiche di Fiverr per i freelance includere temi, modelli o qualsiasi altro elemento che violi i diritti di terzi o le leggi applicabili nell'opera consegnata. Per saperne di più, consulta Guida alla creazione digitale responsabile.

Scopri di più su Daniele T

Daniele T

Junior Penetration Tester Red Team

  • DaItalia
  • Membro dalug 2018
  • Tempo di risposta medio1 ora
  • Lingue

    Italiano, Inglese
I am an offensive-oriented security analyst currently working as a SOC Analyst at a market-leading MSSP. I hold five offensive certifications covering network, web, Active Directory, and cloud penetration testing. I maintain a public technical portfolio on GitHub and aim to transition into a dedicated penetration testing or red team role.