Sfoglia categorie
Italiano
$
USD
Connettiti alla tua IA
Server Security
A short timeline of key events (Premium)
Please remove any secrets before sending. I never ask for server access and never contact the IPs in your logs.
Not sure which package fits? Message me first.A list of suspicious source IPs and usernames (IOCs)
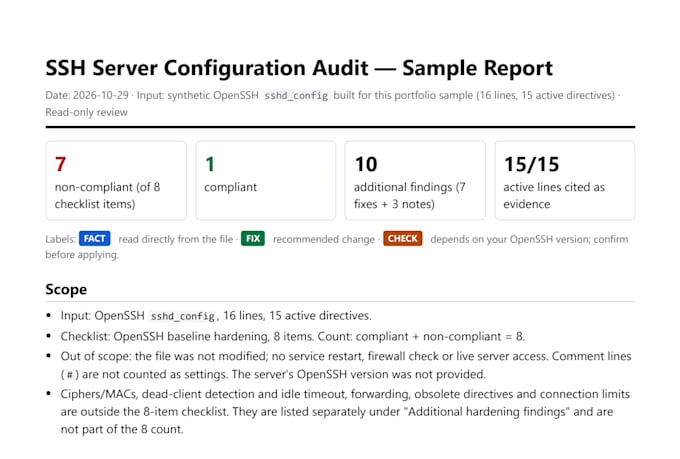
A report with findings ranked by severity, each backed by log evidence
AI-assisted analysis, verified by me before delivery
You receive:
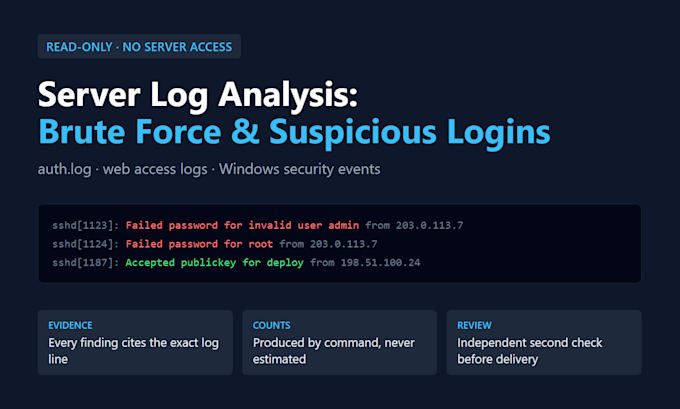
Each report passes an independent second review step before delivery
All counts are produced by command, never estimated
Every finding cites the exact log line and line number
Privilege escalation (sudo) and unusual-hour activity
What makes this different:
Invalid / unexpected usernames being tried
Failed logins followed by a successful one (possible break-in)
Brute-force attempts and the sources behind them
Seeing strange login attempts, or just want to know if your server is under attack?
I review your server log files READ-ONLY (SSH/auth.log, web server access logs, or exported Windows security events) and deliver a clear report of what the logs actually show. Nothing is installed, scanned or connected to: you send the log file, I send back findings.
What I look for:

Sistema operativo:
Windows
•
Linux
•
Unix
Do you need access to my server?
No. I only read the log files you send. No login, no scanning, no connecting to any IP.
Will you block the attackers for me?
No, this gig is analysis only. You get the suspicious IPs/users and clear recommendations; you apply blocks when you are ready.
Is this done by AI?
Analysis is AI-assisted. Every finding must point to a real line in your log, all counts are produced by command, a second independent review step re-checks the report, and I verify it before delivery.
Can you tell me for certain an IP is a hacker?
I report what the logs show (e.g. hundreds of failed logins from one IP). I do not label an IP "malicious" without a source; anything uncertain is marked as such.
What happens to my files?
They are stored privately, used only for your order and deleted on request after delivery.
Do you support Windows servers?
Yes, exported Windows Security event logs too. Message me first so I can tell you which events to export.