Sfoglia categorie
Esplora
Fiverr Pro
Italiano
$
USD
Security Engineer
Are you looking for enterprise-grade threat detection without high software license fees?
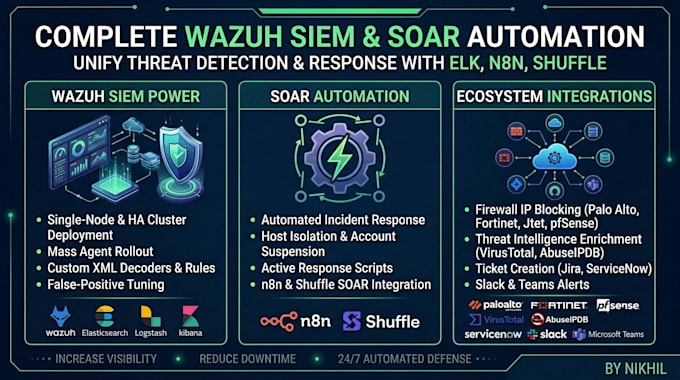
I deliver complete Wazuh SIEM and SOAR automation solutions tailored to your security requirements.
Why Choose My Service?
I help organizations build scalable log management, detect threats in real time, and automate incident response workflows. From initial deployment to complex n8n and Shuffle SOAR integrations, I ensure your environment is fully optimized and audit-ready.
Key Services Offered:
Enhance your security posture with tailored open-source SIEM solutions. Message me today to discuss your infrastructure setup!
Tipo di software:
Altro
What infrastructure or access do I need to provide before starting?
You’ll need to provide root/admin access to a clean cloud instance or server (Ubuntu/RHEL recommended) and API keys or access credentials for any 3rd-party platforms you want integrated (such as firewalls, n8n, Slack, or Jira).
Why should I choose Wazuh over paid enterprise SIEM solutions?
Wazuh is a powerful, open-source SIEM/XDR platform that provides enterprise-grade log monitoring, intrusion detection, and active response without expensive per-agent or data ingestion licensing costs.
Can you integrate Wazuh with my existing firewalls and cloud platforms?
Yes. I can configure syslog ingestion for firewalls like pfSense, Fortinet, and Palo Alto, as well as integrate cloud infrastructure logs from AWS, Azure, or GCP directly into your Wazuh dashboard.
How does SOAR automation with n8n/Shuffle benefit my security operations?
SOAR turns static alerts into automated security actions. Instead of manually reviewing every log, SOAR can automatically block malicious IPs on firewalls, enrich alerts with threat intelligence (VirusTotal), and route tickets to Jira or Slack instantly.
What is Index Lifecycle Management (ILM) and why is it included in Standard?
ILM automates log storage retention and snapshot archiving. It prevents your server disk space from filling up while maintaining fast query performance and ensuring compliance retention policies are met.
Do you offer custom rule creation for non-standard or proprietary apps?
Yes. In the Standard and Premium packages, I write bespoke XML decoders and correlation rules for legacy or custom applications, fully mapped to the MITRE ATT&CK framework.
Will you help tune out false positives so my team isn’t overwhelmed by alerts?
Absolutely. I configure custom silence rules, threshold adjustments, and localized overrides to eliminate noisy alerts so you only get notified about genuine security threats.
Do you provide ongoing 24/7 SOC monitoring after deployment?
No, this service covers engineering, architecture setup, configuration, and automation buildout. Once set up, your internal team can manage the operational alerts directly.
