Sfoglia categorie
Italiano
$
USD
Connettiti alla tua IA
DFIR
Do you suspect a network intrusion, unauthorized data transfer, or malware activity? Let the packets reveal the truth.
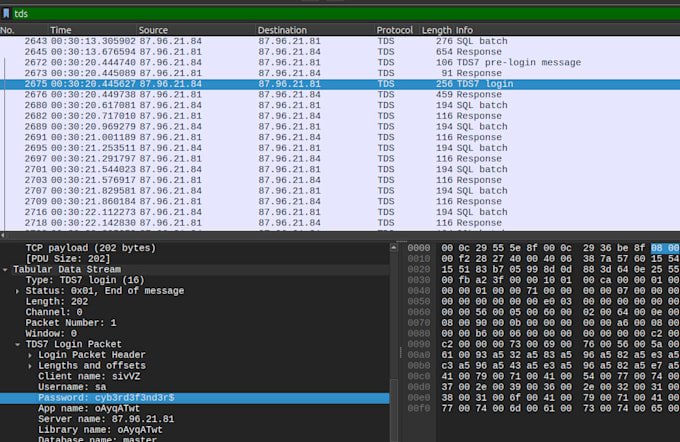
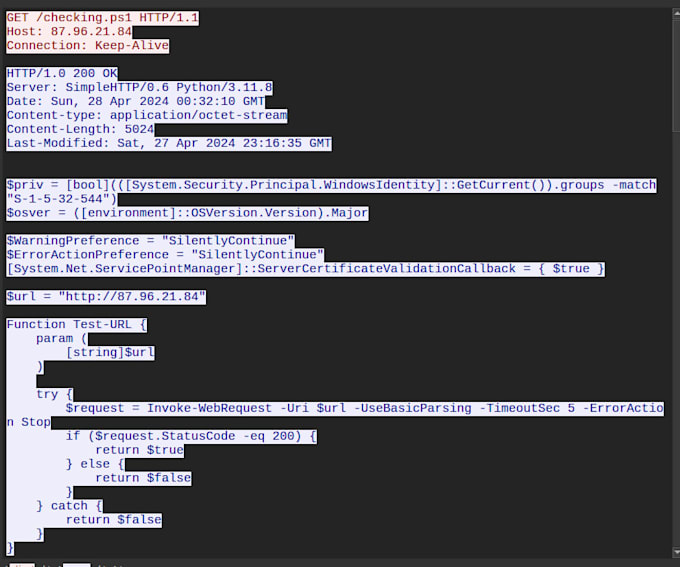
I am a Digital Forensics and Incident Response (DFIR) Specialist. I will perform a deep-dive forensic analysis of your network traffic capture (.pcap / .pcapng) to identify malicious activity, trace attacker movements, and extract actionable Indicators of Compromise (IoCs).
What I Will Investigate:
What You Will Receive:
100% Confidentiality & Strict OPSEC:
All analysis is performed in an isolated environment. NDA available upon request, and all client files are permanently deleted after completion.
**️ Please message me before ordering** to discuss your case and file size!

How do you ensure the confidentiality of my network files and data?
Strict OPSEC and confidentiality are my top priorities. All analysis is performed in an isolated, offline environment. I am happy to sign an NDA upon request, and all client files are permanently deleted immediately after order completion.
What file formats do you accept for analysis?
I accept standard network capture formats including .pcap, .pcapng, and compressed archives (.zip/.rar) containing traffic logs. Feel free to message me before ordering if your file is large.