Alcune informazioni sono riportate in lingua inglese.
Chi sono
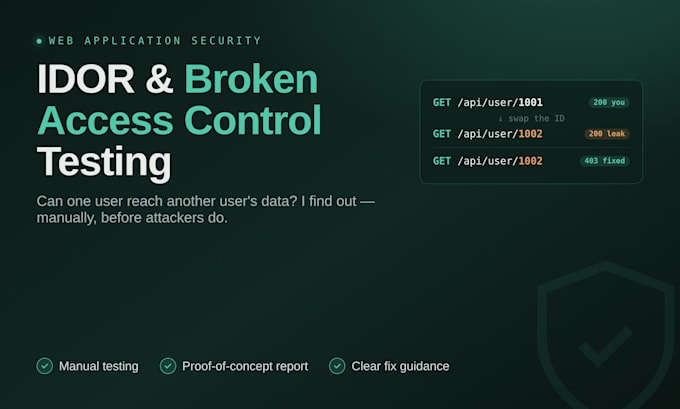
I run quick, honest security checks on apps built with AI tools like Cursor, Claude Code, Lovable, Replit or v0. These tools ship fast but often leave the same basic holes behind: exposed API keys, open endpoints, missing login checks. I look for exactly those — the common, high-risk mistakes near the surface. I'm upfront about my scope: this is a basic check, not a full penetration test. You get a report, and I only test apps you own or are authorized to test.... Continua a leggere