Sfoglia categorie
Italiano
$
USD
Connettiti alla tua IA
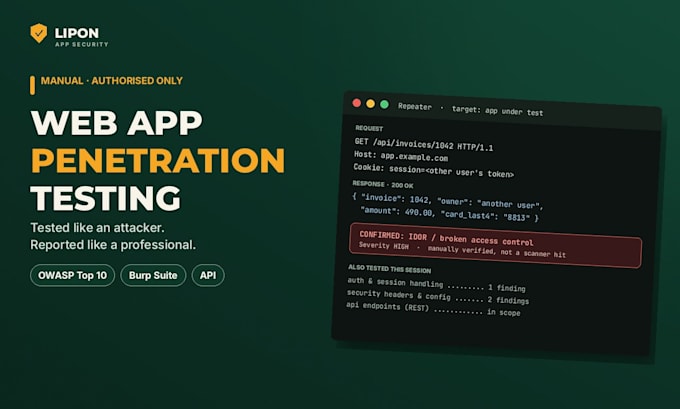
Your web app holds user data, payments and your reputation. I test it the way an attacker would, safely, manually and only with your written authorisation, then show you exactly what to fix.
WHAT I TEST
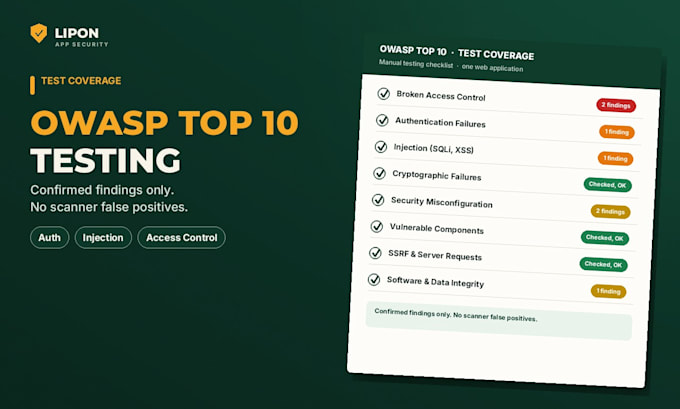
OWASP Top 10: broken access control, authentication and session flaws, injection, security misconfiguration, exposed files and data, vulnerable components, plus your API endpoints. Manual testing with Burp Suite, not just an automated scan.
WHAT YOU GET
A professional report for every confirmed finding: severity, evidence, business impact and a step-by-step fix. Premium adds a full retest after your fixes. See a sample report in my gallery.
WHY ME
Security researcher, TCM Security certified in Practical Ethical Hacking. Non-destructive testing in an agreed window, no DoS, no data damage, and everything stays confidential.
Message me your URL and scope before ordering for a free scope check.
Ricorda che è contrario alle politiche di Fiverr per i freelance includere temi, modelli o qualsiasi altro elemento che violi i diritti di terzi o le leggi applicabili nell'opera consegnata. Per saperne di più, consulta Guida alla creazione digitale responsabile.
Web and AI App Security Researcher, Pentest, OWASP, Supabase RLS
Lingue
Is this legal and safe for my app?
Yes - with your written authorisation and an agreed scope, this is a standard security service. Testing is non-destructive: I do not run denial-of-service attacks, delete data, or disrupt your users, and we agree the testing window together before I start.
What do you need from me?
The target URL, written confirmation that you own the app or are authorised to test it, test accounts for each user role, and any areas that are out of scope. Everything is shared through the Fiverr order requirements only.
What will the report include?
Every confirmed finding with a severity rating, clear evidence, what it means for your business, and step-by-step remediation guidance your developer can follow. Findings are verified manually, so you do not get pages of scanner false positives.
Do you test APIs as well as websites?
Yes. If your web app includes a REST or GraphQL API, tell me in your scope message and I will include authentication, authorisation and data-exposure checks for the API endpoints in the assessment.
Will you retest after we fix the issues?
The Premium package includes a retest of the fixed findings after your team applies the report fixes, plus an updated report showing what is closed and what still needs work.
What do you NOT test?
I do not test systems you do not own, social media or email accounts, and I do not offer denial-of-service, phishing or social engineering services. If you are unsure whether your target is in scope, message me first.
Do you only test apps I own or have permission for?
Yes - I test only systems you own or are authorised to have tested. That is a hard rule of professional penetration testing and protects you legally as well.
Can I see the report format before ordering?
Yes - a full sample report is in my profile's gig gallery (on the vibe-coded app audit gig). Pentest reports follow the same format: findings ranked by severity, evidence, impact and fixes, plus a retest option.