Sfoglia categorie
Esplora
Fiverr Pro
Italiano
$
USD
security check
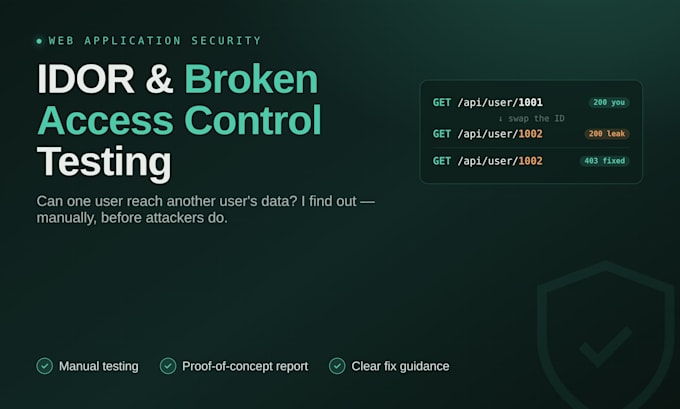
Deeper than a general security scan: this gig is access control only, tested thoroughly (horizontal, vertical & API/BOLA). Most web app breaches don't come from clever exploits they come from a missing permission check. If a logged-in user can change an ID in a URL or API request and see someone else's data, that's an IDOR (Insecure Direct Object Reference) one of the most common flaws in modern apps, and especially in fast-built, no-code and AI-generated ones. I manually test your app for exactly this: can one user reach another user's data, orders, messages, or admin functions? What you get: Manual, hands-on testing of your endpoints not blind scanner spam Horizontal checks (User A User B) and vertical checks (User Admin) A clear PDF report: what's vulnerable, proof of concept, severity, and how to fix it No source code needed. Black-box testing, like a real attacker. Your live app stays intact testing is non-destructive. I only test apps you own or are authorized to test. A short written confirmation is required before I start (template provided after order). Not sure which package fits? Message me your app and I'll tell you honestly before you order.
Will this break or change my app?
No. IDOR testing reads data to prove access — it's non-destructive. I don't alter or delete your records and I use only the minimum proof needed to show a finding.
What is IDOR, in plain terms?
It's when changing an ID — in a URL, a form, or an API call — lets a user reach data that isn't theirs: another customer's invoice, profile, or an admin page. It's very common in quickly-built apps.
Do you need my source code?
No. I test from the outside (black-box), the way a real attacker would, using normal user accounts.
What if you find nothing?
You still get the report — confirming the endpoints tested and that access control held. That's useful proof for you or your own customers. The report is the deliverable either way.
Is this legal?
Yes — when you own the app or are authorized to test it. That's why I require a short written confirmation before I start. I don't test anything without it.
